On this page, you can find the list of our recommendations for Self Host configuration parameters or settings which may improve security and performance.
Configuration recommendations
File upload whitelist
Configuration to enable the specific files to be allowed for the file upload form question types.
Configuration is available only from version 10.0 and above.
Config parameter in the "config.properties" file:
FILE_UPLOADER_WHITELIST
Specify the list of allowed file extensions separated by a comma, for example
FILE_UPLOADER_WHITELIST: jpg,png,gif,pdf
By default, it allows to upload of all files with extensions as
jpg,png,gif,pdf,bmp,svg,ttf,eot,woff,woff2,jpeg,docx,tif,csv,mp4,zip,doc,
eps,mp3,xlsx,tiff,xls,pptx,ico,wmv,psd,txt,ics,msi,ai,otf,mov,ppt,wav,msg,
rar,wma,wmf,xcf,emf,oxps,jfif,xml,xlsm,m4v,pub,rtf,ipa,pdn,ini,avi,
webm,php,thmx,xlsb,pspimage,css,log
Hide server information
Instructions below help you to hide the web server information like server name or version,
which sometimes can be identified as a “Server information Disclosure” potential vulnerability by some scanners.
-
Locate the file %app folder%/keysurvey/app/WEB-INF/web.xml
-
Open it and find "ERROR PAGES" section
-
Add or replace the following rules:
<error-page>
    <error-code>400</error-code>
    <location>/503.html</location>
  </error-page>
  <error-page>
    <error-code>404</error-code>
    <location>/503.html</location>
  </error-page>
  <error-page>
    <error-code>500</error-code>
    <location>/503.html</location>
  </error-page>
-
Add the following lines to the file located at %app folder%/conf/server.xml
-
Open it and locate Host section
-
Add the following rule
<Valve className="org.apache.catalina.valves.ErrorReportValve" showReport="false" showServerInfo="false" />
Set important HTTP headers.
Content-Disposition header
In a regular HTTP response, the Content-Disposition response header is a header indicating if the content is expected to be displayed inline in the browser, that is, as a Web page or as part of a Web page, or as an attachment, that is downloaded and saved locally.
Instructions on how to set headers for IIS on Windows
https://learn.microsoft.com/en-us/troubleshoot/developer/webapps/iis/development/add-http-response-header-web-site
Settings recommendations
Restrict direct link access to form responses
The user right enables the restriction for the direct link access to form responses when enabled.
When enabled, users cannot access the form response (RBR) by the direct link.
Configuration is available only from version 10.0 and above.
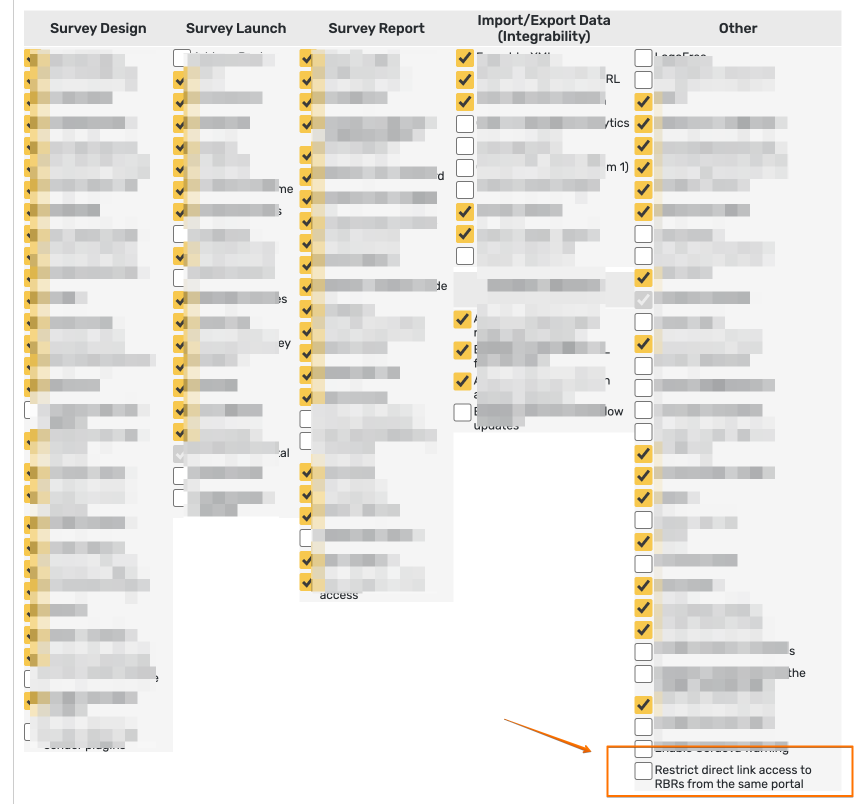
By default, it’s disabled - which means authorized users able to access the form responses
The rights are applied per account, so to enable it for multiple accounts, it’s required to enable it for each account’s rights.
Disable scripts
The user right enable or disable the scripts on the forms.
Disable item script - For the users that have this right disabled, the system strip out all 'script' tags from any form element.
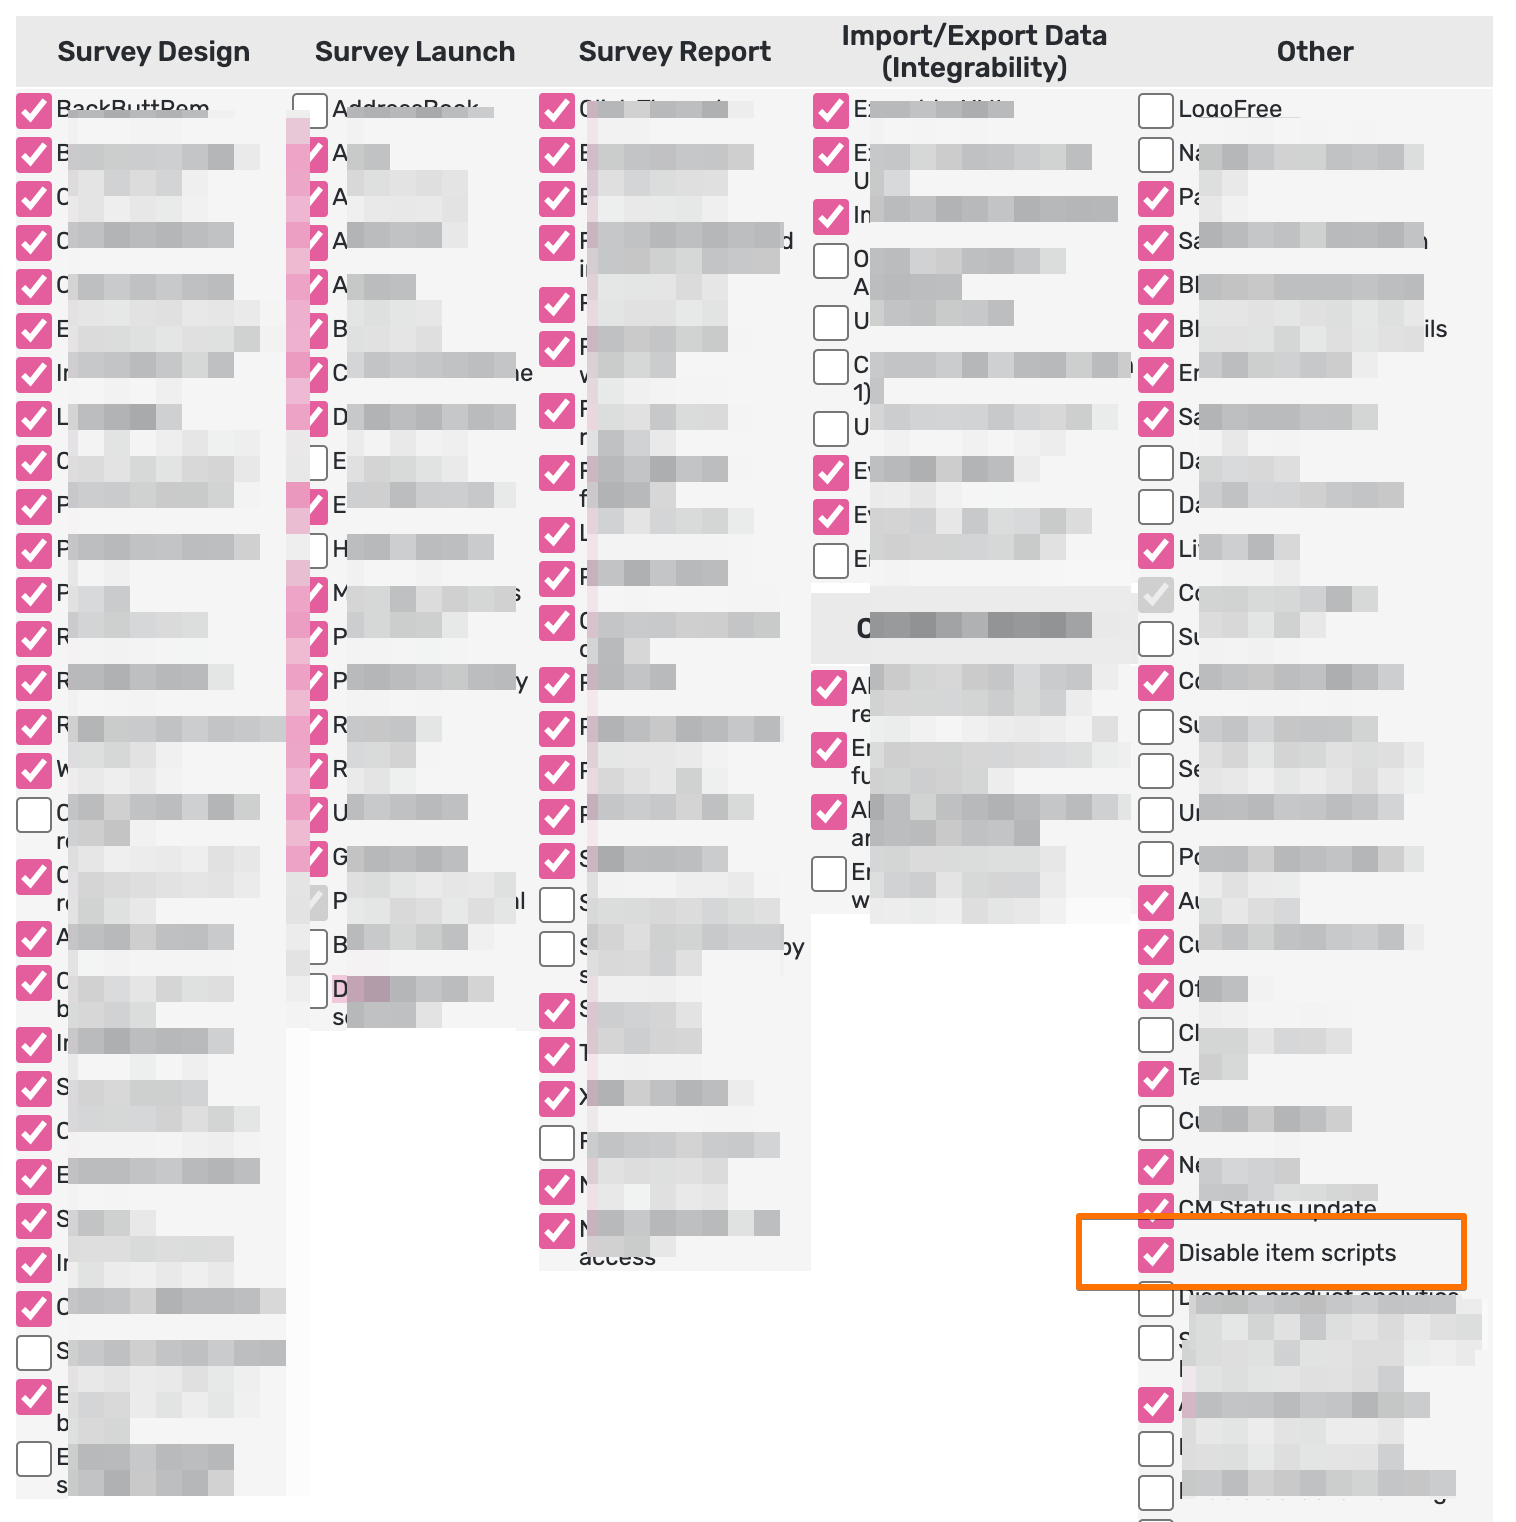
The rights are applied per account, so to enable it for multiple accounts, it’s required to enable it for each account’s rights.
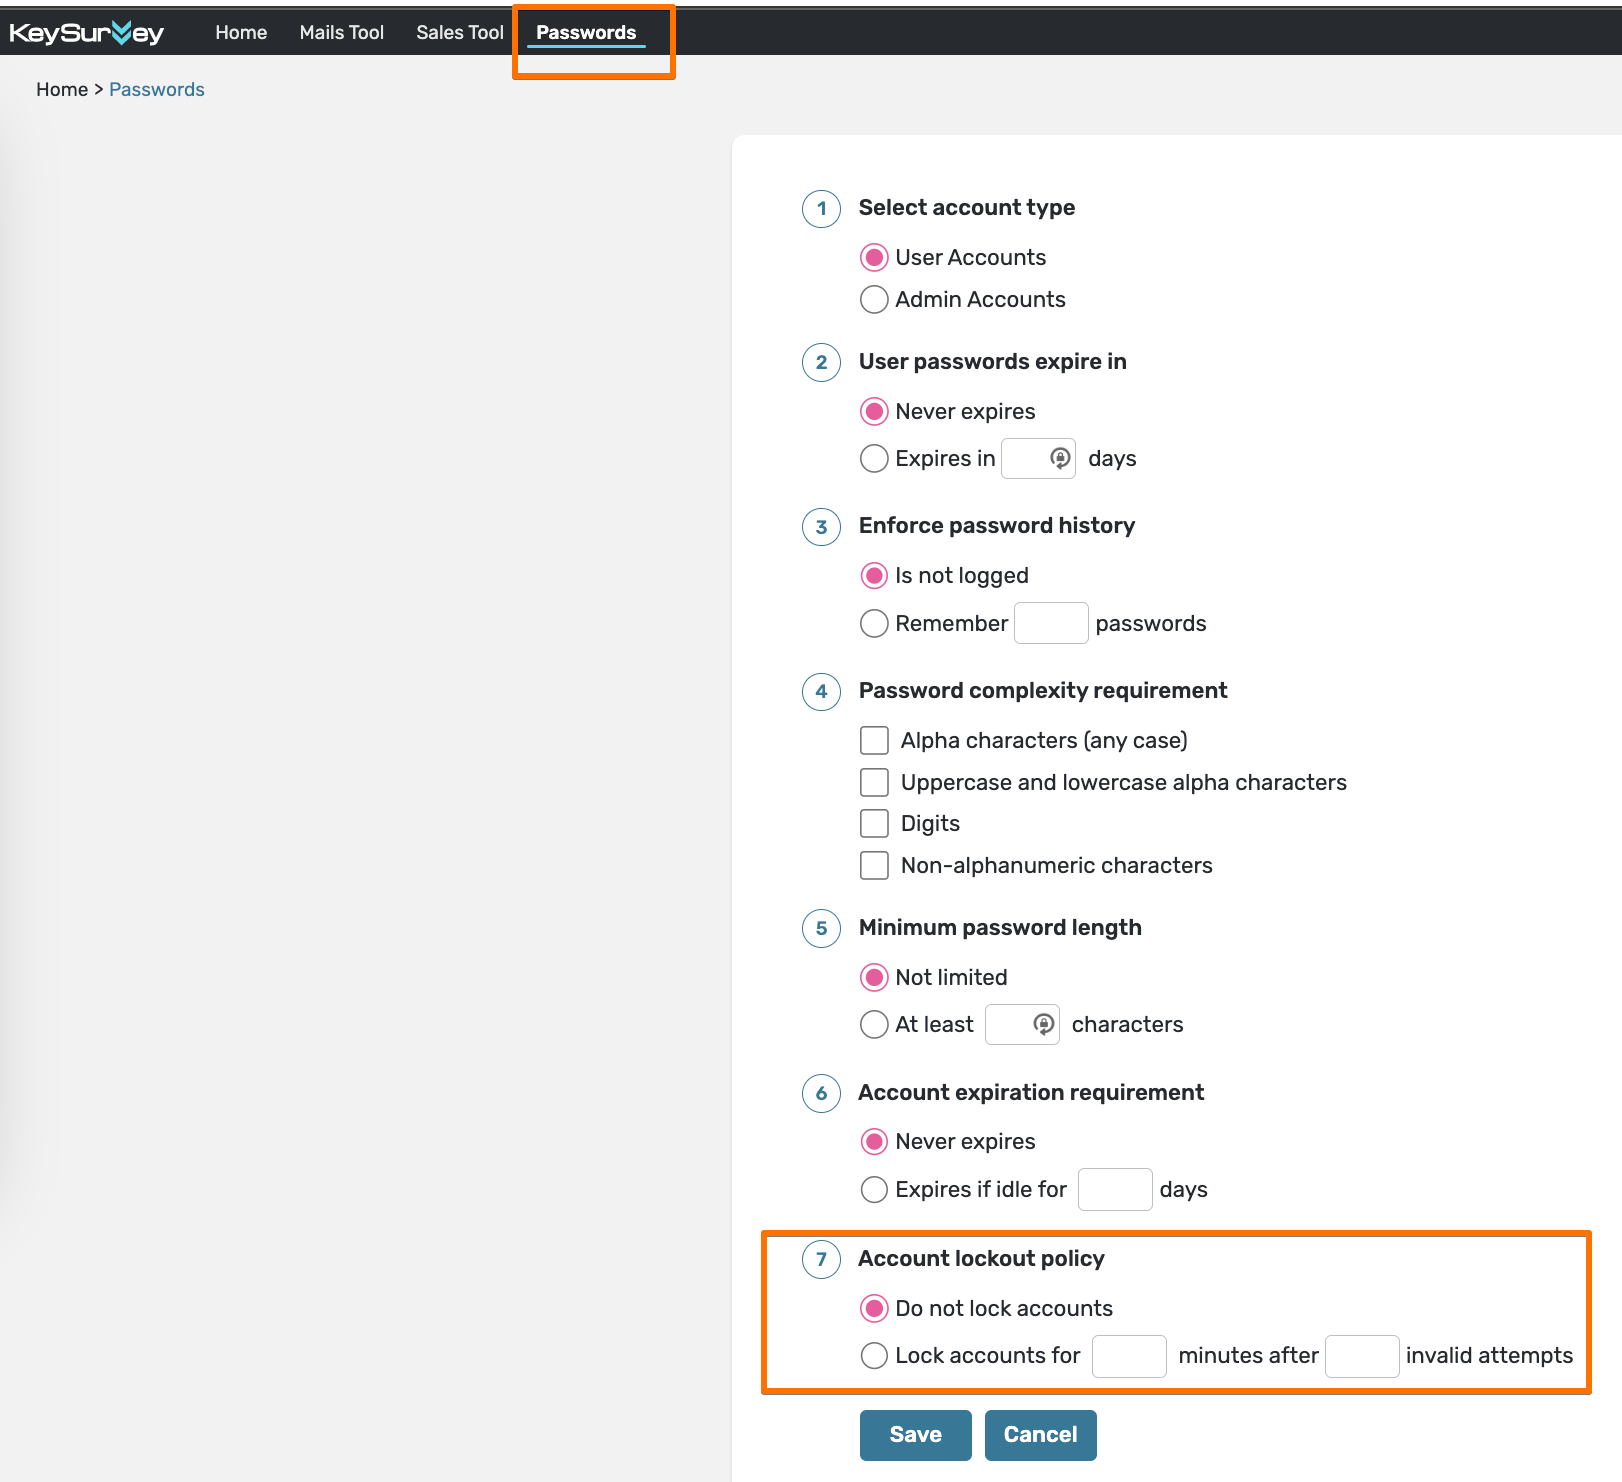
Accounts lockout policy
When enabled, the system will lock the accounts after some invalid login attempts.